Arg Box
One appliance, full visibility. Arg Box reads the traffic, logs, configuration and behaviour of your servers, spots the anomaly and stops it before it becomes an incident.
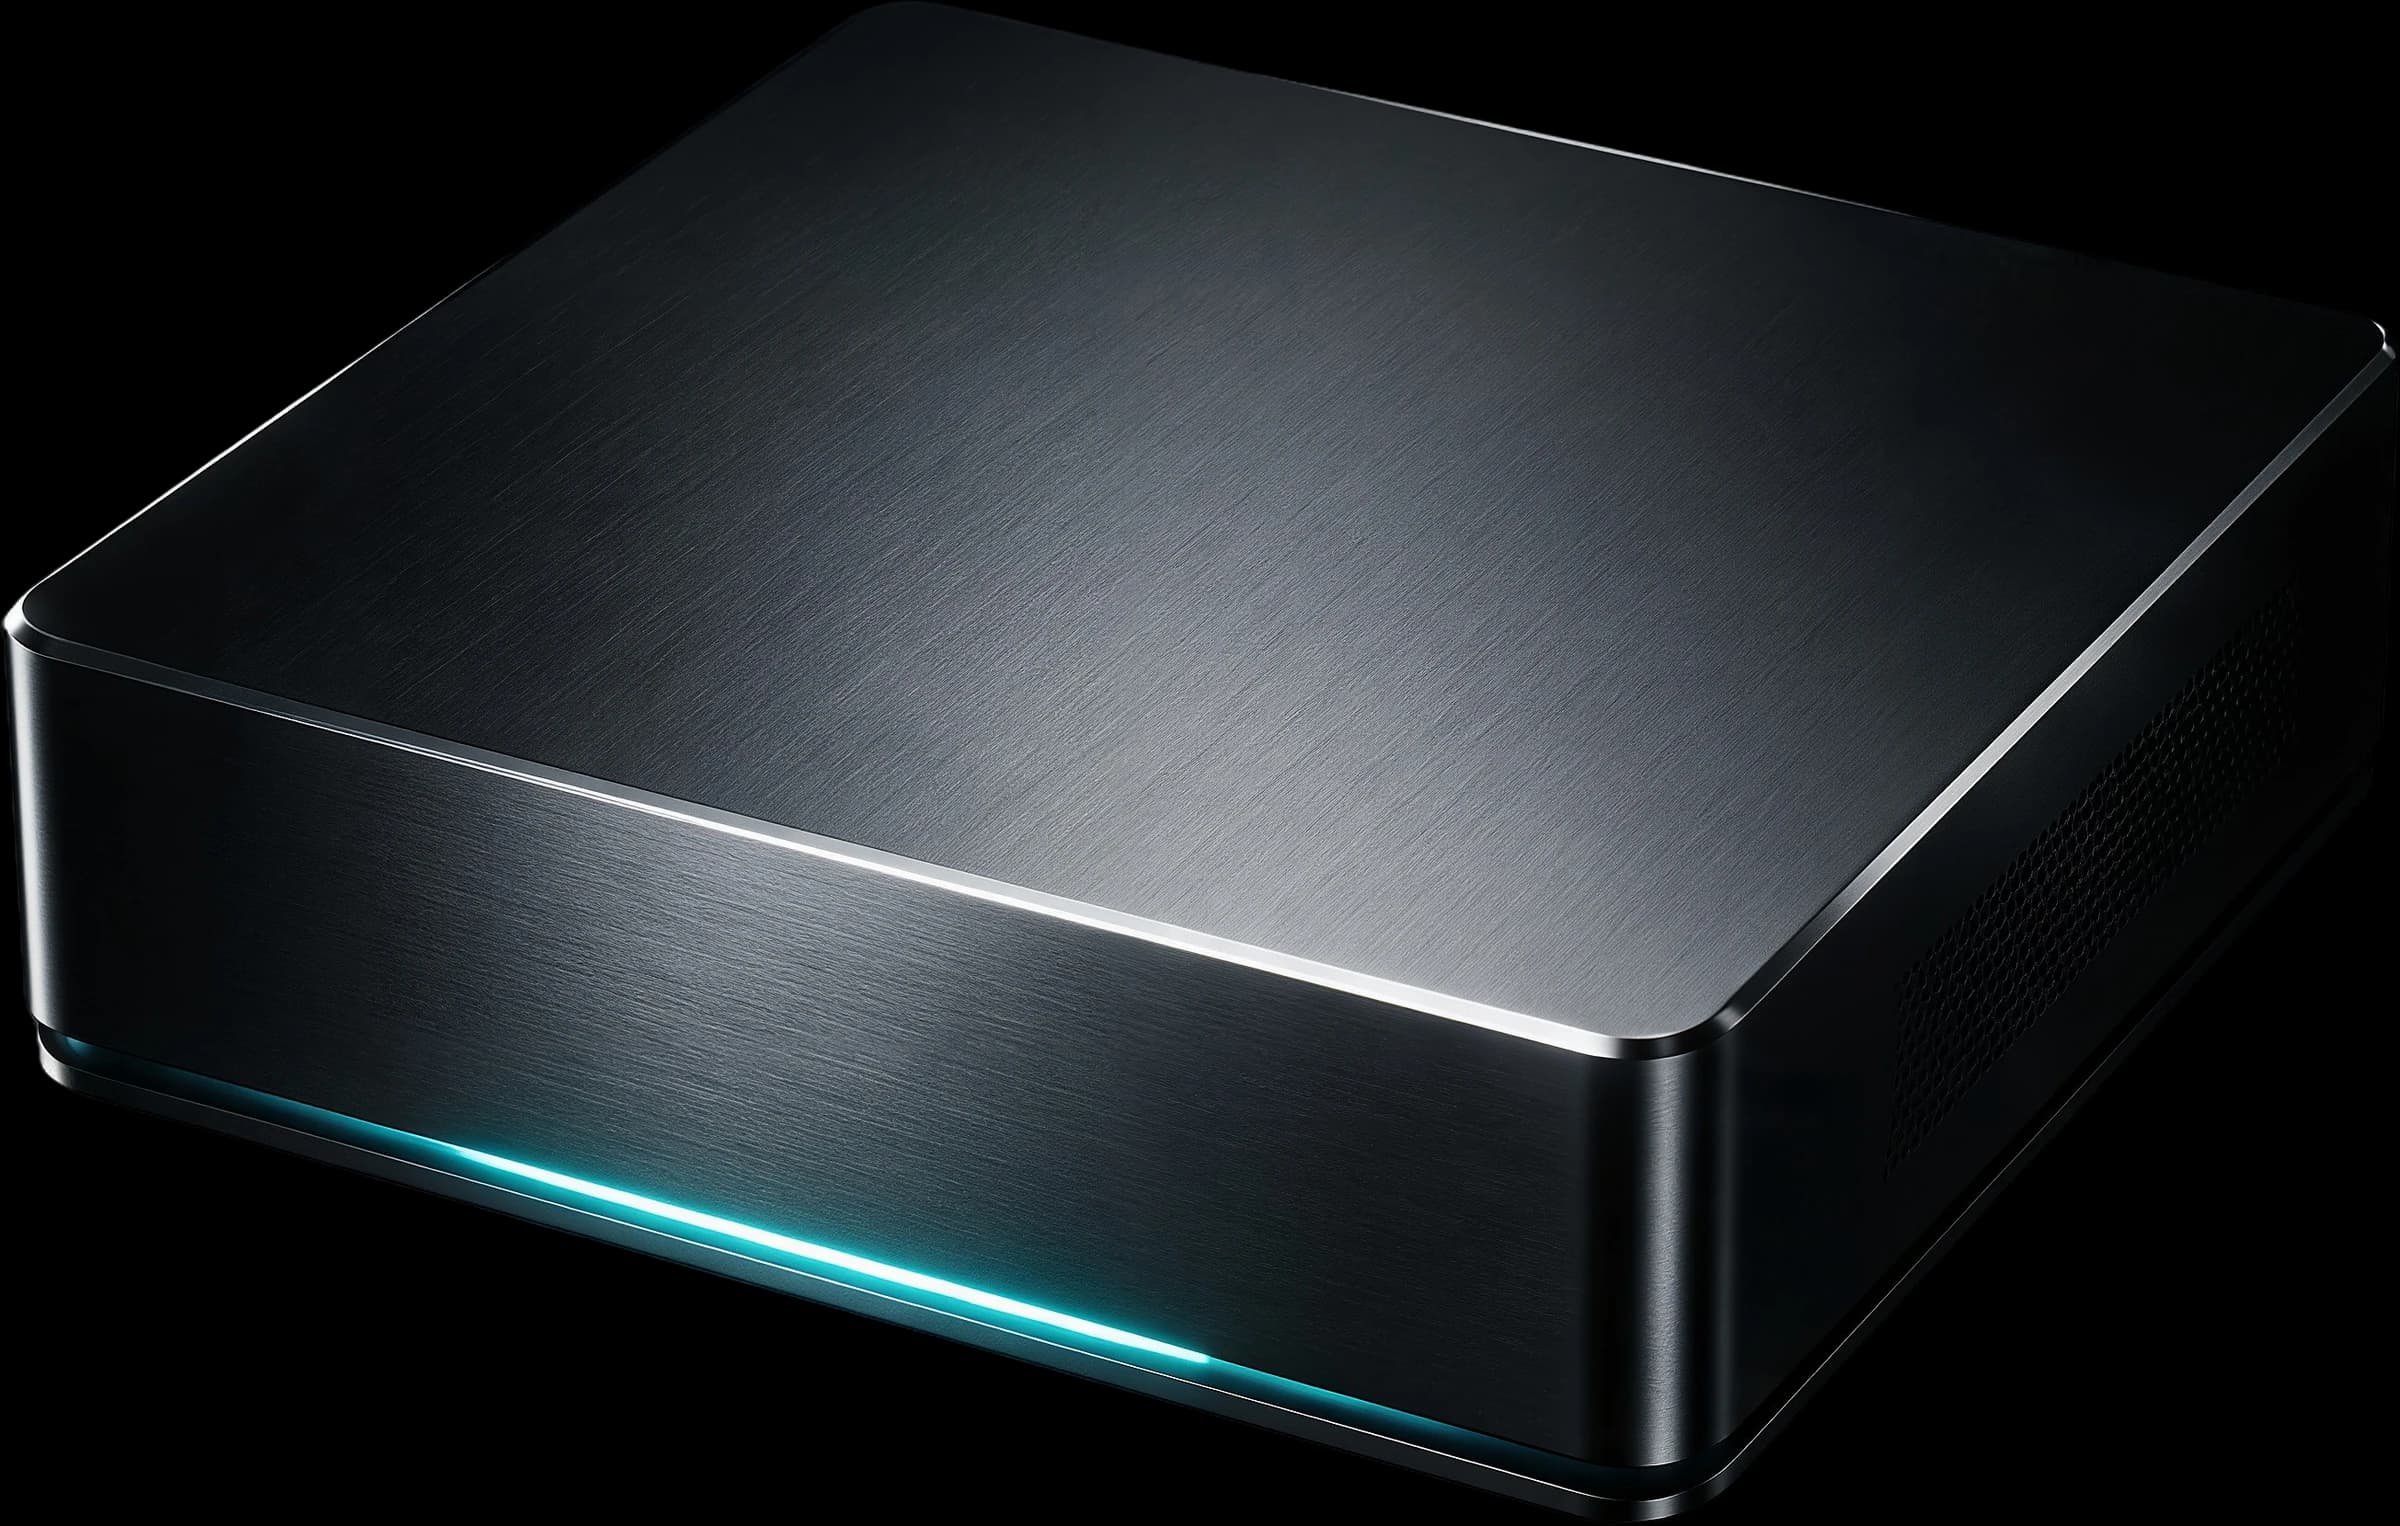
- Processor
- Core i7, 13th gen
- Memory, by plan
- 16–32 GB
- Encrypted NVMe
- Up to 1 TB
- Networking
- 4 × 2.5 GbE
What used to take a full rack, in the footprint of a book
Network intrusion detection
Deep packet inspection on a Suricata engine, current signature feeds and custom rules tuned to your architecture.
Server monitoring
Lightweight agents report file integrity, configuration drift and suspicious process behaviour from every server.
Central log custody
Collection, normalisation and digitally signed retention — ready for audit and post-incident forensics.
Automated response
Definable containment playbooks: block an IP, quarantine a host, revoke a session, page the team.
Vulnerability management
Scheduled asset scanning, CVE correlation and patch prioritisation based on real exposure rather than raw score.
Compliance reporting
Audit-ready reports for internal review and common frameworks, exportable as PDF or over the API.
How it sits in your network
Arg Box listens passively on a mirror (SPAN) port and communicates actively with its agents. No new single point of failure is added to the data path.
- 1
Collection layer
Mirror port, syslog, server agents, cloud APIs and firewall feeds.
- 2
Analysis layer
Rule engine plus behavioural model, event correlation and risk scoring.
- 3
Response layer
Playbook execution, firewall and orchestrator integration, multi-channel alerting.
- 4
Presentation layer
Live dashboard, scheduled reporting and an API for your existing tooling.
No alert does not mean you are safe
Most tools only speak when they see something. That is exactly the weakness: a capable attacker works to make sure nothing is seen. Arg Box treats silence as an event too.
No system catches everything. That is why every plan includes an on-call engineer: the tooling finds the gap, a person decides what it means.
Silence is itself an event
Every agent's heartbeat is counted. If one stops reporting for a few minutes — even if it comes back healthy — that gap is recorded as an event, with the exact time it opened and closed.
A real outage is not mistaken for tampering
A failed cable has its own signature: the link drops, every device on that port goes quiet at the same moment and returns together. Agent tampering looks different: one host is silent while its switch port is still passing traffic. Because Arg Box watches the network independently of the agents, it can put the two accounts side by side.
Gradual intrusion is found by looking backwards
An attacker stays undetected for a median of 14 days, rising to 122 days in espionage cases. You do not catch that on day one; you catch it the day a new indicator is published and you can search your own history for it. That is what log retention in your plan really buys: how far back you are able to look.
Killing the agent does not blind us
Arg Box sits outside the host, on a mirror port. To blind it, an attacker has to reach a separate physical device with TPM 2.0 and secure boot — not just stop a Windows service.
Arg Box is not sold separately
The appliance is part of the service. Every plan includes an Arg Box configured to match, and maintenance, updates, repair and replacement on failure are ours — at no separate cost.
- 01
The configuration is chosen from your size
Processor, memory, node count and log retention differ between plans. A short audit before installation establishes which configuration actually fits you.
- 02
A one-week evaluation, on your own server
Before any commitment we run an evaluation build on a virtual machine inside your own infrastructure. You see the dashboard, the alerts and the detection logic without any hardware changing hands.
- 03
The evaluation is not the whole appliance
It runs on a virtual machine, so it has no TPM-backed identity, no secure boot with your own key, and no power or rack-environment sensing. What you see is the software; the hardware layer only exists on the appliance itself.
The full detail
Memory, storage, monitored devices and data retention depend on the plan, and come from the same numbers as the pricing page. Everything else is the same on every unit.
By plan
Compare the plans in full| Specification | Watch | Protect | Operate |
|---|---|---|---|
| Monitored devices | Up to 25 devices | Up to 75 devices | Up to 200 devices |
| Memory | 16 GB | 32 GB | Sized to your network |
| Storage | 512 GB | 1 TB | Sized to your network |
| Data retention | 90 days | 180 days | 365 days |
Compute & storage
- Processor
- Intel Core i7, 13th gen
- Disk
- NVMe, encrypted at rest
- Array
- Optional RAID 1 configuration
Networking
- Ports
- 4 × 2.5 Gigabit Ethernet
- Placement
- On a mirror (SPAN) port, outside your servers
Physical & security
- Dimensions
- 240 × 175 × 55 mm
- Power draw
- 28 W typical, 65 W peak
- Cooling
- Fanless aluminium chassis — completely silent
- Root of trust
- TPM 2.0 and secure boot with your own keys
Who it is built for
Mid-sized companies
Small technical team, serious infrastructure. Arg Box acts as a full-time security analyst.
Service providers
Monitor multiple clients from one console, with full data isolation and per-tenant reporting.
Sensitive environments
Where data is not permitted to leave the building — everything stays on local hardware.
Arg Box, in three plans
All three plans ship the same complete device. What changes is the size of the network, the depth of the analysis, and how much of the work we do for you.
See it first, then decide
An evaluation build runs for a week on your own server so you can see the dashboard, the detection logic and the output up close — no hardware to install, no commitment.